Full capability,
inside your perimeter
Meet your security and compliance needs without trading away capability. Overcut runs wherever your infrastructure standards require.
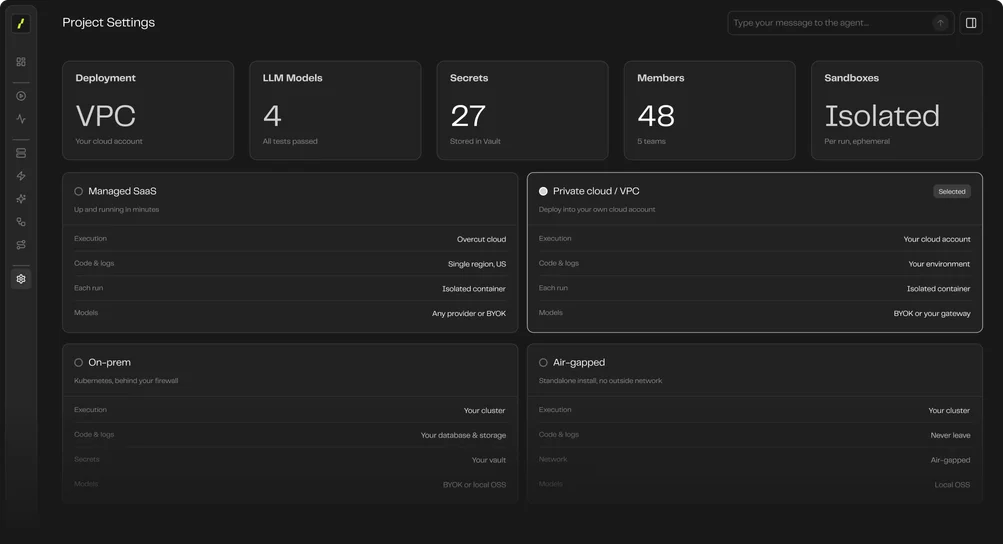




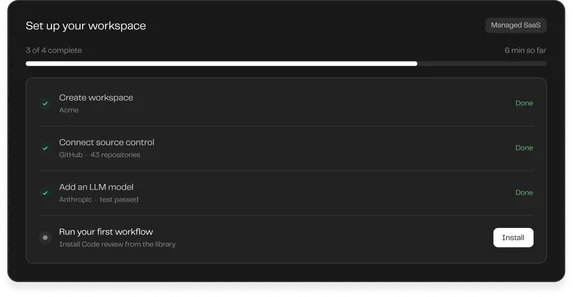
Fully managed SaaS
Up and running in minutes. We run the control plane; you connect your tools and ship.
Capabilities
- Up and running in minutes
- Managed control plane
- Connect your tools
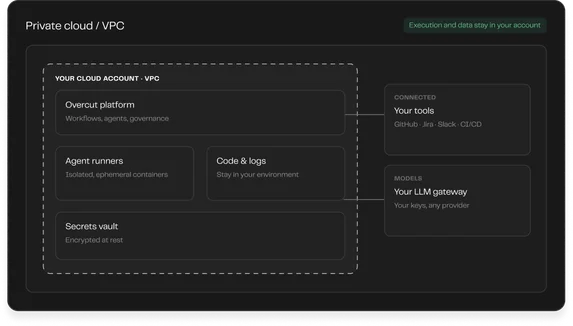
Private cloud / VPC
Deploy into your own cloud account so execution and data stay in your environment.
Capabilities
- Your cloud account
- Execution in your environment
- Data in your environment
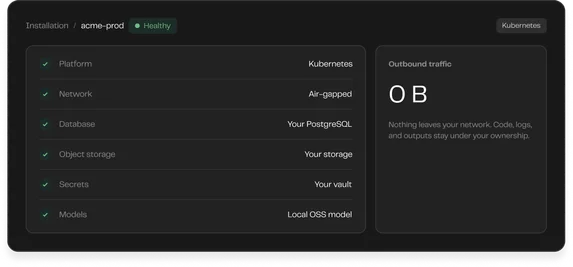
On-prem & air-gapped
Run entirely behind your firewall for the strictest data-residency requirements.
Capabilities
- Behind your firewall
- Data residency
- Air-gapped networks
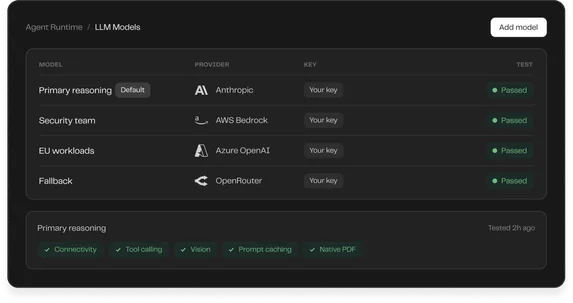
BYOK / BYOM
Bring your own model keys and route across providers or local models. You stay in control.
Capabilities
- Anthropic
- OpenAI
- AWS Bedrock
- Azure OpenAI
- Local OSS models
- Your LLM gateway
“Overcut transformed our ad-hoc code reviews into a standardized, CI/CD-driven workflow.”
3x
faster review turnaround
100%
of merges through one workflow

Security on
your terms
Align Overcut with your internal infrastructure and policy standards.
See enterpriseYour infrastructure
- #1
Sandbox execution
Isolated, ephemeral environments with no cross-run interference.
- #2
Data residency
Keep code, logs, and outputs inside your security perimeter.
- #3
Encrypted in your perimeter
Secrets live in an encrypted vault, with encryption at rest throughout.
- #4
No vendor lock-in
Overcut works alongside your stack instead of replacing it.
Your keys & identity
- #5
BYOK / BYOM
Bring your own model keys and route across providers or local models.
- #6
Scoped tokens
Least-privilege credentials for every integration and action.
- #7
Enterprise SSO & directory
SAML and OIDC single sign-on with LDAP and Active Directory sync.
- #8
Security & compliance fit
Align with your internal infrastructure and policy standards.


Your AI software factory starts with one command
The same AI everyone has. Run with the security, control, and scale enterprises actually require.
Questions teams ask
How can we deploy Overcut?
As fully managed SaaS, in your own private cloud or VPC, or fully on-prem on Kubernetes, including standalone and air-gapped installs.
Where do our code and data live?
In the deployment you choose. With private cloud and on-prem, code and agent activity never leave your environment, and on-prem can run on your own database, storage, and secrets.
Which models can we use, and can we bring our own?
Route across Anthropic, OpenAI, AWS Bedrock, Azure OpenAI, or local OSS models per workflow or per agent. Bring your own keys, or point Overcut at your own LLM gateway for a single budget.
Can we start in the cloud and move on-prem later?
Yes. The same platform, controls, and integrations apply across every deployment option, so you can move in-house later without re-learning the product.
Is each run isolated?
Every run executes in an isolated, ephemeral container that is destroyed when it finishes.
